
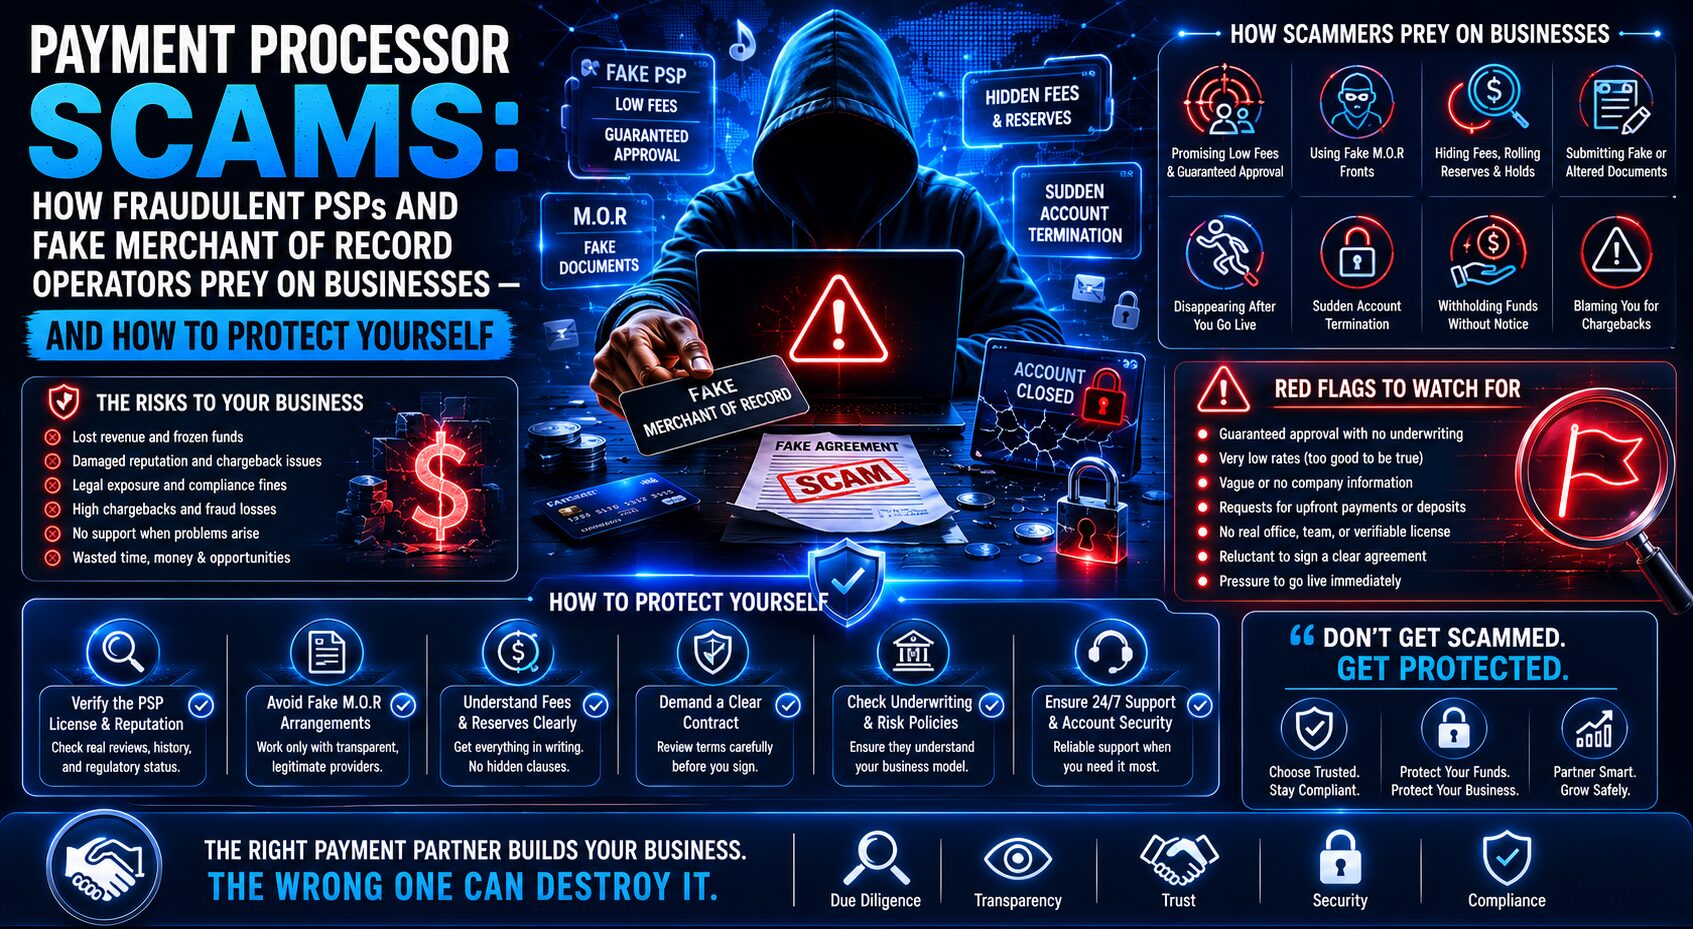
How Fraudulent PSPs and Fake Merchant of Record Operators Prey on Businesses — And How to Protect Yourself
The global e-commerce fraud losses are projected to rise to $43.6 billion by 2027, up from $33.2 billion in 2025. Inside that staggering number is a category of fraud that is routinely underreported, poorly understood, and specifically targeted at the merchants themselves rather than their customers: fraudulent payment processors, fake PSPs, and predatory merchant of record operators who exploit the desperation and information asymmetry of high-risk businesses to extract fees, steal processing funds, and vanish with revenue that took months or years to generate.
This is not a marginal or theoretical risk. Some of the biggest names in payments have been caught red-handed. Worldpay quietly tacked on undisclosed fees of up to 1.95% — hitting some small businesses for hundreds of dollars every month. Vantiv, later acquired by Worldpay, settled a lawsuit after allegedly overcharging nearly 200,000 merchants. If established household names engage in predatory fee practices, the risk from smaller, unregulated, and deliberately fraudulent operators is exponentially higher.
For high-risk merchants — businesses in iGaming, forex, adult content, CBD, nutraceuticals, cryptocurrency, and other sectors that struggle to access mainstream payment processing — the vulnerability is acute. The combination of urgency (needing payment processing to operate at all), limited options (mainstream processors refuse the category), and limited industry knowledge (unfamiliarity with what legitimate processing looks like) creates exactly the conditions that fraudulent operators exploit.
This article is an exhaustive, fully researched warning guide. It covers every major category of payment processor fraud targeting merchants — from petty setup fee theft to the most sophisticated Merchant of Record scams that steal hundreds of thousands of dollars in processing revenue — with specific red flags, real-world patterns, and the complete due diligence framework that protects businesses from each type.
Part 1: The Predatory Fee Landscape — How Legitimate-Looking Processors Rob Merchants Slowly
Before examining outright fraud, every merchant must understand the legal-but-predatory fee practices that bleed businesses through opacity and contractual complexity. These practices are the gateway through which genuinely fraudulent operators launder the appearance of legitimacy — because the line between “aggressive commercial practices” and “fraud” is precisely where bad actors operate.
The Hidden Fee Architecture
Merchant services scams have evolved, and in 2025, they’re more sophisticated than ever. Scammers target small businesses with misleading contracts, fake low rates, and deceptive sales tactics. They hide behind Google Ads, AI-written reviews, and vague pricing structures.
The hidden fee structure works through tiered misdirection. A processor advertises a headline rate — “2.9% + $0.30” or “3.5% for high-risk businesses” — that sounds competitive and specific. What the merchant does not see until they examine their first statement is the layered fee architecture beneath: monthly minimum fees (you pay the difference if your transaction volume is below a monthly minimum), PCI non-compliance fees (charged if the merchant has not completed PCI DSS self-certification, often without notification that this is required), non-qualified surcharges (additional percentage points applied to transactions that the processor categorises as “non-qualified” using criteria not disclosed at signing), batch fees, statement fees, regulatory compliance fees, gateway access fees charged separately from the processing rate, and annual “account review” fees that appear without contractual basis.
Some processors will hold a portion of your deposits, called a reserve, without clearly disclosing it. This is common in high-risk industries but can also happen when processors abuse risk rules. Watch for unexplained “risk reserves” or withheld payouts and zero transparency in contract terms.
The combined effect of these fees is that a merchant who signed up expecting to pay 4% per transaction finds themselves paying an effective rate of 6%–9% when all fees are included in the calculation — a difference that, at $500,000 annual processing volume, represents $10,000–$25,000 in additional annual cost that was never disclosed at signing.
The PCI Compliance Fee Trap
One of the most systematically abused fee categories is PCI DSS compliance. Legitimate processors charge a PCI compliance fee that covers the cost of the merchant’s annual self-assessment questionnaire and any scan requirements. Predatory processors charge a “PCI non-compliance fee” — a monthly penalty of $20–$50 — as a permanent fee stream, without ever notifying the merchant that compliance is achievable through a self-assessment, or providing any assistance in completing it. The merchant pays the non-compliance fee indefinitely, believing it is a standard processing cost, while the processor profits from the merchant’s non-completion of a process they have not explained.
Long-Term Contract Traps With Punitive Exit Terms
Some processors push their exclusive POS software, promising it can handle everything your business will face. The catch? The POS only works with their processing service instead of integrating with the system you’re already using. Then once you’re locked in, the terms are revealed.
Contract lock-in with punitive early termination fees is a systematic practice among predatory processors. A merchant signs a three-year processing agreement with a $500–$5,000 early termination fee, discovers the actual fees are far higher than represented, attempts to leave, and faces a bill that makes switching economically painful. The processor has effectively monetised the switching barrier rather than earned the merchant’s business through competitive performance.
Part 2: The Setup Fee and Onboarding Fee Scam — Pure Theft Disguised as Processing
The setup fee and onboarding fee scam is one of the most straightforward and pervasive forms of outright fraud targeting merchants — particularly high-risk merchants who have been refused by multiple legitimate processors and have begun to interpret any approval offer as an opportunity worth paying for.
How the Setup Fee Scam Operates
The pattern is consistent and identifiable once you know what to look for. A website — typically professionally designed, with convincing testimonials, familiar payment brand logos, and claims of specialist expertise in high-risk categories — advertises merchant account services. It ranks prominently in Google search results for terms like “high-risk merchant account approval” or “instant merchant account approval” — often through paid advertising rather than organic authority. They hide behind Google Ads, AI-written reviews, and vague pricing structures.
The merchant applies. The “processor” reviews the application and returns a positive response — an approval that mainstream processors have declined to provide. The catch: an upfront “setup fee,” “application fee,” “compliance fee,” or “onboarding fee” of $200–$2,500 must be paid before the account is activated. The fee is typically framed as covering underwriting costs, bank onboarding, account configuration, or technical integration.
The merchant pays. And then one of two things happens: either the account is never activated and the “processor” becomes uncontactable, or a rudimentary account is set up that proves non-functional, at which point the processor cites technical or compliance reasons for delays — requesting additional fees to resolve each manufactured obstacle — until the merchant either gives up or escalates to dispute the charge.
A merchant account scam is designed to be appealing to new merchants and startups, especially high-risk merchants. As the saying goes, if it seems too good to be true, it probably is.
The Fake Onboarding Process as Data Theft
A more technically sophisticated variation combines setup fee theft with identity and banking credential theft. Some scam sites pose as processors and collect your banking info during a fake onboarding process. This is often tied to aggressive online ads offering “no-fee processing” or “instant approval.” The site looks real, but lacks SSL, business address, or verified contact info. You are asked to provide your bank login. Once submitted, your data is stolen or sold.
The merchant submits banking details, KYB documentation, and personal identification to what they believe is a legitimate processor’s secure onboarding portal. The “processor” harvests this data — company bank account details, director identification, beneficial ownership information — and uses it for identity fraud, business account takeover, or sale on dark web marketplaces. Nearly 1,200 scam domains were linked to fraudulent merchant accounts, with most registered in the United Kingdom.
The sophistication of these fake onboarding portals has increased significantly through 2024 and 2025. Scammers are even figuring out how to automate the process of setting up their own fake retailers, allowing them to trick consumers and businesses into handing over payment credentials. AI-generated company profiles, fabricated regulatory registration numbers, and stolen SSL certificates from legitimate financial institutions are now standard components of advanced fake PSP operations.
Part 3: The Fake PSP Gateway Scam — Intercepting Your Customers’ Payments
The fake PSP gateway scam operates at the customer-facing payment level rather than the merchant onboarding level. It is more technically sophisticated and financially damaging than setup fee fraud — because it does not just take the merchant’s onboarding fee, it intercepts the actual payments that the merchant’s customers make.
The Malicious Code Injection Variant
Many e-commerce sites choose to offload payment card charges to third-party payment service platforms. Cybercriminals have developed fake payment service platforms that highly resemble legitimate PSPs. Rather than infecting a merchant’s checkout page with malware that skims information after it has been inputted, cybercriminals infect the merchant site by adding a line or two of code which redirects the user to a fake PSP at the time of purchase.
What makes this scam so stealthy? Apart from swapping legitimate payment processing sites with fraudulent ones, cybercriminals closely mimic the traits of real e-banking pages to further trick the user into believing their purchase is secure. The fake payment processing page checks all the fields once the user completes them and informs the user if the field is invalid. This particular scam redirects users from the fake PSP back to the legitimate payment site after their information has already been accepted.
For the merchant, this attack is almost invisible at the point of occurrence: the customer apparently completes checkout, the order appears to have been placed, but the payment was made to a fraudulent processor rather than the legitimate one. The merchant ships the goods — or provides the service — while receiving no payment. The customer’s card is charged by the fraudulent processor. The customer eventually notices, disputes the charge, and the cardholder receives a refund — leaving the merchant with neither the goods nor the payment, and facing a chargeback penalty on top.
There were 10,500 such hacks active in 2025, leading to the compromise of over 23 million online transactions.
Protecting Against Gateway Injection Attacks
Advanced scams involve malicious code injections into payment pages, redirecting customer payments to third parties. Protection requires: using PCI-DSS-compliant gateways only; enabling two-factor authentication for gateway access; and running regular site security scans for malware and JavaScript injections. For merchants integrating third-party payment forms, verifying the payment form’s domain and SSL certificate before every processing session — through manual inspection and automated monitoring tools — is the technical control that catches injection attacks before they generate sustained losses.
Part 4: The Merchant of Record Scam — The Most Dangerous Fraud Pattern of 2025
The most financially devastating payment processor fraud targeting merchants is the Merchant of Record (MoR) scam — a sophisticated scheme where an entity presents itself as a PSP or payment aggregator but operates as a fraudulent Merchant of Record, pooling multiple merchants’ processing volumes under a single acquiring relationship before vanishing with the aggregated settlement funds.
Understanding the Legitimate MoR Model
To understand the fraud, it is necessary to understand the legitimate model it mimics. A Merchant of Record model consolidates all digital commerce insights into a single location, giving companies a holistic view from which to manage and run their business. A genuine MoR takes on legal liability for the transaction — handling payment collection, tax remittance, fraud management, and compliance on behalf of the software or content vendor. Legitimate MoR operators include well-established platforms like Paddle, FastSpring, and Cleverbridge, which operate transparently, are regulated, and maintain direct relationships with their underlying acquirers that are disclosed to the merchants they serve.
How the Fraudulent MoR Scam Operates
The fraudulent MoR operator — presenting as a PSP, payment aggregator, or specialist high-risk payment processor — approaches merchants who cannot access direct acquiring relationships. The pitch is compelling: we will handle your payment processing under our acquiring relationship, settle funds to you after our commission, and manage all the compliance complexity.
What the merchant does not know is that the “processor” does not have a direct acquiring relationship of their own with a licensed acquiring bank. Instead, they have opened a single merchant account with a real acquirer — using their own company as the registered merchant — and are routing multiple client merchants’ transactions through this single account as a sub-merchant aggregation scheme.
Merchant identity fraud involves criminals setting up a merchant account on behalf of a seemingly legitimate business and charging stolen credit cards. The hackers then vanish before the cardholders discover the fraudulent payments and reverse the transactions. When this happens, the payment facilitator is liable for the loss.
The fraudulent MoR operator collects card payments from the merchants’ customers, which settle into the single master account the operator controls. The operator remits a proportion of the settlements to each merchant initially — building trust and encouraging merchants to increase their processing volumes. Then, at a moment of maximum processing volume — often timed to coincide with peak trading periods — the operator ceases remittances, transfers the accumulated settlement balance out of the account, and becomes uncontactable. The merchant is left with no access to their customer payment funds, no recourse against the fraudulent operator, and an acquiring bank that has no contractual relationship with them.
The Bust-Out Fraud Variant
Bust-out fraud occurs when fraudsters build trust with potential victims over time in anticipation of stealing as much as possible in one final heist, before disappearing. They pay bills on time and maybe even sell and deliver goods to customers. Then, once they are ready, they bust out. Having a merchant account helps the fraudster establish the legitimacy of their business.
In the payment processor context, the bust-out variant involves the fraudulent MoR operator building a credible track record over months — settling funds promptly, providing responsive customer service, offering competitive rates — specifically to encourage merchants to concentrate their entire payment volume through the operator’s system. The operator systematically increases the volume flowing through the single master account, knowing that the eventual theft will be proportional to the volume they have managed to attract before the bust-out.
The timing of the bust-out is calculated. Operators typically choose periods immediately following a business’s peak trading season — when the maximum accumulated settlement balance is held in the master account — or periods when merchants are least likely to notice immediate anomalies (Christmas period, August holiday, regulatory reporting cycles). By the time merchants identify that settlements have stopped and escalate, the operator has typically moved funds to cryptocurrency wallets or overseas accounts, making recovery through civil channels extremely difficult.
Real-World Scale of the MoR Scam Problem
Billions vanish each year through digital payment fraud schemes that lure with apparent legitimacy before stealing funds. While aggregate statistics specifically for fraudulent MoR operations are not publicly maintained, the Recorded Future 2024 Annual Payment Fraud Intelligence Report confirms the systemic nature: nearly 1,200 scam domains were linked to fraudulent merchant accounts. Each of these domains represents a potential entry point for fraudulent aggregation schemes that may be operating MoR-style fraud at the time of identification.
In 2024, Operation First Light was an international law enforcement operation executed by 61 countries targeting online scammers. The operation resulted in 3,950 arrests and identified 14,643 other suspects. While Operation First Light targeted a range of scam types, payment processing fraud was a significant component — reflecting the international law enforcement community’s recognition that fraudulent payment infrastructure represents one of the highest-value and most technically sophisticated fraud categories in the current threat landscape.
Part 5: The Sub-Aggregator Trap — Hidden Liability for Merchants
Beyond the outright fraud of the MoR scam, legitimate-appearing but non-compliant sub-aggregation schemes create indirect liability for merchants that can result in account termination, MATCH listing, and fund seizure — without the merchant having done anything fraudulent themselves.
How Sub-Aggregator Arrangements Create Merchant Risk
When a merchant processes through a “processor” that is itself operating as a sub-merchant under a Payment Facilitator’s (PayFac’s) master merchant account, the merchant’s transactions are subject to the PayFac’s portfolio-level risk management decisions — not just their own account’s performance. If the PayFac’s portfolio collectively breaches card network programme thresholds (Visa VAMP, Mastercard BRAM), the PayFac may face account restrictions that affect all sub-merchants simultaneously — including merchants with clean individual processing records.
High-risk accounts may be subject to holds triggered by specific conditions. Unusual transaction volumes, sudden spikes in chargeback rates, or other anomalies can prompt the processor to temporarily freeze settlements while they investigate. When these holds are triggered at the PayFac level rather than the individual merchant level, the merchant has no visibility, no notice, and no recourse within the timeframe that matters operationally.
The merchant who discovers their processing has been frozen because of another merchant’s fraud — routed through the same master account by a non-compliant aggregator — finds themselves in an extremely difficult position: unable to process payments, unable to access their own settlement balance during the investigation, and potentially associated with fraud activity through the shared account relationship they did not know they were party to.
Part 6: The 20 Red Flags Every Merchant Must Know
The common thread across every fraudulent payment processing scheme is that they are identifiable in advance, by merchants who know what to look for. The following red flags are drawn from documented fraud patterns, industry security reporting, and the specific characteristics that distinguish fraudulent operators from legitimate ones.
Red Flag 1: Upfront setup, application, or onboarding fees before account activation. Legitimate processors do not charge significant upfront fees before your account is active and processing. Application review costs are minimal or absorbed by the processor as a cost of customer acquisition. A request for $200–$2,500 before any account is operational is a strong indicator of a fee-extraction scam.
Red Flag 2: Too-good-to-be-true rates for your category. If your business has been declined by multiple processors and a new provider offers rates significantly below the range you have encountered elsewhere — 2% for a business category that typically processes at 5%–7% — the rate is almost certainly either misrepresented, will change dramatically after initial processing, or is a bait to capture your setup fee.
Red Flag 3: No verifiable regulatory registration. In the UK, payment service providers must be authorised or registered with the FCA. In the US, legitimate acquiring relationships involve banks registered with federal or state regulators. Look up the provider’s registered business entity and processor sponsor. If you cannot independently verify the processor’s regulatory standing through the FCA register, FDIC TheFinRate, or equivalent official source, the processor is either unregulated or non-existent as a regulated entity.
Red Flag 4: The company cannot name its acquiring bank. Every legitimate payment processor has a direct relationship with at least one acquiring bank — and will typically disclose this relationship. A processor that cannot or will not name its acquiring bank, or that gives vague answers about its “banking partners,” is either concealing a sub-aggregator arrangement that creates the hidden liability risks described above, or has no genuine acquiring relationship at all.
Red Flag 5: Website domain registered recently or with hidden WHOIS. Payment processors with genuine industry standing have established web presences with multi-year domain registration histories. A domain registered within the past six to eighteen months, or with WHOIS privacy protection hiding the registrant’s identity, warrants significant additional due diligence before any fee payment or account application.
Red Flag 6: Pressure to process quickly or accept verbal terms. Legitimate processors understand that merchant account decisions involve significant due diligence and are comfortable with deliberate review processes. Fraudulent operators create artificial urgency — “this rate is only available for the next 48 hours,” “our compliance team has approved you but we need the setup fee by tomorrow” — because their scheme depends on the merchant acting before due diligence is completed.
Red Flag 7: No physical address or verifiable business premises. The vast majority of fraudulent payment processors operate without verifiable physical premises. Check the company’s registered address against Companies House (UK) or state corporation databases (US). Verify SSL (“https://” and padlock icon) before submitting info. Never share banking credentials on unknown forms.
Red Flag 8: Contract terms not available in writing before fee payment. Any payment processor that asks for a setup fee before providing a written contract for review is either hiding contractual terms that would cause the merchant to decline, or does not have a contract at all — because the “account” they are offering does not exist.
Red Flag 9: Settlement delays that are not contractually explained. Legitimate processors specify their settlement timelines in contract. Extended settlement delays, unexplained holds, and “under review” settlement statuses that persist beyond the contractually specified period are indicators of either inadequate operational infrastructure or deliberate settlement withholding in the buildup to a bust-out.
Red Flag 10: No direct contact with the actual acquiring bank. If a merchant has been processing for three or more months through a processor and still has no direct communication channel with, or independent confirmation from, the underlying acquiring bank — the processor is operating as a non-transparent intermediary that creates the exact liability and recovery risk that the MoR scam exploits.
Red Flag 11: Requests for bank login credentials during onboarding. No legitimate payment processor requires your banking login credentials during onboarding. Account verification for settlement purposes is conducted through micro-deposit verification or bank statement submission — not by asking for your online banking username and password.
Red Flag 12: Testimonials and reviews that cannot be independently verified. AI-generated reviews on fake review sites, testimonials with stock photography portraits, and Google Ads-driven search results that place the provider above legitimate industry sources are the standard marketing infrastructure of fraudulent PSPs. They hide behind Google Ads, AI-written reviews, and vague pricing structures.
Red Flag 13: Processing volumes growing faster than stated business justification. For merchants participating in aggregated processing schemes, a processor that encourages rapid volume growth — offering better rates for higher volumes, removing reserve requirements as volume increases — may be deliberately building the aggregated balance that represents the eventual theft target.
Red Flag 14: Contract terms require arbitration in obscure offshore jurisdictions. Legitimate UK and US payment processors specify dispute resolution in their home jurisdiction. Contracts requiring arbitration in jurisdictions with limited legal cooperation with UK and US courts — or “international commercial arbitration” without specifying the arbitral institution — are designed to make legal recovery prohibitively expensive.
Red Flag 15: No PCI DSS compliance documentation. Any payment processor handling card data must be PCI DSS compliant and should be able to provide their current Attestation of Compliance or Service Provider listing on the Visa/Mastercard network databases. A processor that cannot produce this documentation — or provides documentation that cannot be verified against the card network’s published Service Provider lists — is not operating compliant payment infrastructure.
Red Flag 16: Processing rate changes mid-contract without notice. Legitimate processors provide contractual rate locks or advance notice of rate changes. Processors that increase rates without notice, or introduce new fees without contractual basis, are either contractually non-compliant or operating without a genuine contract.
Red Flag 17: Settlement amounts that do not reconcile with processing reports. Even before a full bust-out, fraudulent processors typically skim settlement amounts — remitting slightly less than the contractual amount to the merchant, attributing the difference to fees, reserves, or chargebacks without adequate documentation. Merchants who do not reconcile settlement amounts against processing reports do not detect this theft until the differences are substantial.
Red Flag 18: The provider claims to be a “payment gateway” but cannot identify a separate acquiring bank. A payment gateway is a technology product — it captures and transmits transaction data. An acquiring bank is the licensed financial institution that actually settles the funds. A “gateway” that also holds your settlement funds without identifying an underlying acquiring bank is operating as an unlicensed quasi-bank — creating regulatory exposure for the merchant and direct theft risk for settlement balances.
Red Flag 19: Requests for cryptocurrency or wire transfer for setup fees. Legitimate processors accept payment for setup fees through standard business payment channels — business credit card, ACH, or corporate cheque. A request for setup fee payment via cryptocurrency or international wire transfer removes the merchant’s ability to dispute the charge if the account is never delivered — because cryptocurrency transactions and international wires are not reversible through card network dispute processes.
Red Flag 20: No verifiable complaints resolution history. Check the provider against the Better Business Bureau (US), Trustpilot, Google Reviews, and financial services complaint registers. The complete absence of any review history for a processor claiming years of operation is as concerning as a pattern of unresolved complaints — because fraudulent processors operate for short periods under specific brand names before reconstituting under new names after exposure.
Part 7: Due Diligence Framework — Verifying a Payment Processor Before Signing
The following verification framework provides a systematic process for evaluating any payment processor before providing sensitive information, paying fees, or signing contracts.
Regulatory Verification
In the UK: search the FCA Financial Services Register (register.fca.org.uk) for the provider’s legal entity name. A legitimate payment processor will appear as an authorised Payment Institution (PI) or registered Small Payment Institution. If the provider is not on the register, it is either unregulated — which is itself a disqualifying finding — or is claiming to operate under another entity’s licence, which requires direct verification with that entity.
In the US: search the FDIC BankFind database for the acquiring bank identified by the processor. Verify the processor’s registration as a Payment Facilitator with Visa and Mastercard through their respective published Service Provider lists. Non-bank payment processors operating in the US must be registered with FinCEN as Money Services Businesses — search the MSB Registrant Search for the provider’s legal entity name.
Corporate Verification
Search Companies House (UK) or the Secretary of State corporation database in the relevant US state for the provider’s registered company. Verify: date of incorporation (recently incorporated companies warrant additional scrutiny); registered address (matches the address used on the website and in communications); filing history (legitimate businesses maintain annual filings; dormant or filing-delinquent companies are warning signs); and beneficial ownership (the beneficial owners of the company should be publicly traceable and should not include individuals associated with known payment processing fraud).
Contract Review
Before paying any fee or providing sensitive information: obtain a complete draft contract in writing; review all fee schedules including all named fees and any “fees as determined by processor” catch-all clauses; verify the contract identifies the acquiring bank by name; confirm the settlement timeline and the contractual process for resolving settlement disputes; and confirm early termination terms and the absence of multi-year lock-in with punitive exit fees.
If the processor declines to provide a written contract before fee payment, disengage immediately. This is a non-negotiable requirement.
Reference Verification
Request references from three to five merchants in your category who have processed through the provider for at least six months. Contact those references independently — not through contact details provided by the processor — and ask specific questions: Have settlements been received consistently and on time? Has the processing rate matched the quoted rate? Has the processor been responsive to support requests? Have there been any unexplained holds or reserve changes?
Part 8: What to Do If You Have Already Been Victimised
If you have paid a setup fee and received no account, or if a processor has withheld your settlement funds, the following steps should be initiated immediately.
Dispute the Setup Fee Payment
If the setup fee was paid by credit or debit card, initiate a chargeback through your card issuer immediately — citing “services not rendered” as the dispute basis. Provide the card issuer with: documentation of the fee payment, the processor’s failure to deliver the account, and any communications demonstrating that the service was not provided. The UK’s mandatory APP fraud reimbursement scheme — in effect from 7 October 2024, requiring sending PSPs to reimburse all consumers who fall victim to APP fraud — may apply if the fee was paid via bank transfer through Faster Payments.
Report to Regulatory Authorities
In the UK, report fraudulent payment processors to Action Fraud (actionfraud.police.uk), the FCA (fca.org.uk/consumers/report-scam), and the Payment Systems Regulator. In the US, report to the FBI’s Internet Crime Complaint Center (IC3.gov), the FTC (reportfraud.ftc.gov), and your state Attorney General’s consumer protection division. These reports contribute to the intelligence databases that law enforcement agencies use to identify and prosecute fraudulent operators — and establishing a formal complaint record is essential if you pursue civil recovery.
Preserve Evidence
Before the fraudulent processor’s website and communications are taken down — which typically happens within days to weeks of exposure — capture and preserve: all website screenshots; all email and chat communications; the contract or terms presented at onboarding; all bank statements and card statements showing fee payments; and any processing reports or settlement statements received. This evidence is the foundation of both criminal reports and civil recovery actions.
Legal Recovery Options
Civil recovery from fraudulent payment processors operating across international borders is difficult but not impossible. UK merchants have access to the Small Claims Court for disputes up to £10,000, and County Court for higher values. US merchants can pursue civil claims in state or federal court. Where fraudulent operators have moved funds to cryptocurrency wallets, blockchain forensics firms can in some cases trace and assist in recovery — though success rates depend on the speed of action and the sophistication of the operator’s laundering procedures.
Part 9: Regulatory Developments That Provide New Protection in 2025–2026
Several regulatory developments in 2025 have strengthened the protective framework for merchants in the UK and US.
UK APP Fraud Mandatory Reimbursement
The reimbursement requirement came into effect on 7 October 2024. Sending PSPs must reimburse all consumers who fall victim to APP fraud. For merchants who were deceived into authorising bank transfers to fraudulent payment processors — including setup fees paid via Faster Payments — the mandatory APP fraud reimbursement scheme provides a recovery pathway that did not previously exist. The sending PSP is required to reimburse the merchant (treated as a consumer for APP fraud purposes in most cases) and the cost is shared with the receiving PSP.
According to the Payment Services Regulation 2024, if a PSP has reasonable grounds to believe a payment is fraudulent, it can delay payments for up to four business days. This delay power enables banks to pause payments to known or suspected fraudulent processor accounts — a protective mechanism that operates upstream of the merchant’s payment decision.
FCA Authorisation as Due Diligence Foundation
The FCA’s ongoing enforcement of Payment Institution authorisation requirements means that operating payment processing services in the UK without FCA registration is itself a criminal offence. Merchants who verify FCA authorisation before engaging any processor can be confident that the provider is subject to FCA supervision, capital requirements, safeguarding obligations for client funds, and conduct-of-business rules — all of which provide structural protections against the MoR scam and settlement withholding.
Operation First Light and International Enforcement Cooperation
Operation First Light 2024 was an international law enforcement operation executed by 61 countries targeting online scammers, resulting in 3,950 arrests and identification of 14,643 other suspects. The scale and coordination of this operation demonstrates that fraudulent payment processing operations are now a primary target of international law enforcement rather than a peripheral concern. Merchants who report fraud quickly — before operators can transfer funds and dissolve — contribute to enforcement operations that may recover their funds and prevent future victims.
Conclusion: The Payment Processing Industry Has a Predation Problem — and Knowledge Is the Defence
The payment processing industry operates on information asymmetry. Processors understand their own fee structures, contract terms, and operational capabilities far better than the merchants who depend on them. Fraudulent operators exploit this asymmetry systematically — using the appearance of technical complexity, regulatory opacity, and high-risk merchants’ limited options to extract fees, misrepresent services, and ultimately steal processing revenue.
The defence is knowledge. A merchant who understands the legitimate structure of payment processing — what fees are normal, what regulatory credentials are required, what contractual terms are acceptable — is a merchant who recognises fraud when it is presented to them. The twenty red flags in this article represent the accumulated intelligence from documented fraud patterns, regulatory reports, and industry security research. Applied consistently, they will stop the vast majority of fraudulent processors at the due diligence stage — before any money changes hands.
The most important principle is simple: no legitimate payment processor requires significant upfront fees before your account is operational, no legitimate processor will refuse to name their acquiring bank, and no legitimate processor will decline to provide a written contract for review before you commit to anything. These are not negotiating positions — they are minimum standards that every merchant should enforce without exception.
Frequently Asked Questions (FAQ)
Q1: Is it normal for a payment processor to charge an upfront setup fee before activating my account?
No — and this is one of the clearest red flags in the payment processing industry. Legitimate high-risk payment processors recover their onboarding costs through the processing fees they charge on live transactions, not through upfront payments. Some processors charge a one-time activation fee after the account is operational and processing has begun, which is legitimate and transparent. Any processor requesting $200 or more before your account is active and confirmed by your acquiring bank should be treated with extreme caution. Paying a setup fee to an unverified processor and receiving no account in return is one of the most common forms of payment processor fraud, specifically targeting high-risk merchants who have been declined elsewhere and are motivated by urgency.
Q2: How do I verify whether a payment processor is legitimately authorised in the UK or US?
In the UK, search the FCA Financial Services Register (register.fca.org.uk) using the provider’s full legal entity name — not their trading name. A legitimate UK payment processor will appear as an Authorised Payment Institution or Registered Small Payment Institution. In the US, verify that the underlying acquiring bank is FDIC-registered (fdic.gov/bank/individual/failed/banklist), check the processor’s registration as a Payment Facilitator on Visa’s and Mastercard’s published Global Registry of Service Providers, and search FinCEN’s MSB Registrant database for non-bank processors. If the provider cannot be independently verified through these official sources, do not share sensitive information and do not pay any fees.
Q3: What is a Merchant of Record scam and how does it differ from standard payment processor fraud?
A Merchant of Record (MoR) scam is a sophisticated fraud in which an entity presents itself as a PSP or payment aggregator but actually pools multiple merchants’ processing volumes under a single acquiring relationship that the fraudulent operator controls. Rather than stealing a one-time setup fee, the MoR fraudster processes weeks or months of genuine customer transactions across multiple merchant clients, accumulating a large settlement balance in the master account they control before disappearing. The fraud is particularly damaging because it targets merchants’ actual sales revenue — not just onboarding fees — and is typically timed to maximum processing periods. The distinguishing characteristic is that the fraudulent operator is the named merchant on the acquiring bank relationship, meaning the actual merchants have no direct contractual relationship with the acquiring bank and no recovery rights against that institution.
Q4: What should I do if a payment processor is withholding my settlement funds?
Act immediately on three fronts simultaneously. First, send a formal written notice to the processor — by email with read receipt and by recorded delivery to their registered address — demanding settlement of the outstanding balance within seven days and citing the specific contractual settlement terms they are in breach of. Second, report to the FCA (UK) or your state’s financial regulator (US), providing all documentation of the processing relationship and the withheld funds — regulators can compel information disclosure and in some cases freeze assets faster than civil courts. Third, if the processor is FCA-authorised, file a complaint with the Financial Ombudsman Service (UK) — the FOS can require regulated firms to release improperly withheld funds within its complaint resolution process. Do not wait to see if settlement arrives — every day of delay in reporting reduces the likelihood of fund recovery.
Q5: How can I identify whether a “payment processor” is actually operating as an undisclosed sub-merchant under another acquirer?
Ask the processor directly, in writing: what is the name of your acquiring bank, and are you operating as a direct merchant on that acquiring bank’s system or as a sub-merchant under a payment facilitator? A legitimate processor will answer this question clearly and can provide documentation of their direct acquiring relationship. If the processor deflects, provides vague answers about “banking partners,” or is unable to provide a specific acquiring bank name, they are almost certainly operating as a sub-merchant aggregator without direct acquiring relationships. This arrangement creates hidden risk for you: your account’s performance is subject to portfolio-level decisions by the entity above you in the chain, and you have no contractual relationship with the actual acquiring bank.
Q6: What legal recourse is available to a merchant who has lost money to a fraudulent payment processor in the UK?
UK merchants have several recourse pathways depending on how the fraudulent payment was made. If setup fees were paid by credit card, a Section 75 Consumer Credit Act claim may apply for amounts between £100 and £30,000. If paid by Faster Payments bank transfer on or after 7 October 2024, the mandatory APP fraud reimbursement scheme applies — contact your sending bank immediately and file an APP fraud claim citing the fraudulent processor. For settlement fund theft above the Small Claims Court threshold of £10,000, County Court proceedings against the processor’s registered entity are available — though effectiveness depends on whether the entity has UK assets. Report simultaneously to Action Fraud, the FCA, and the National Crime Agency’s cybercrime reporting portal. For international fraud involving cryptocurrency transfers of stolen funds, the City of London Police’s specialist payment fraud unit accepts referrals.
Q7: Are high-risk merchant accounts from unverified providers legitimate if they are processing successfully for the first few months?
Initial successful processing is a hallmark of the bust-out fraud pattern, not evidence of legitimacy. Fraudulent processors and MoR operators deliberately operate successfully — settling funds promptly, providing responsive service, offering competitive rates — for an initial period specifically to build trust and encourage merchants to concentrate increasing volumes through the fraudulent operator’s system. The bust-out is timed to occur when the accumulated settlement balance reaches maximum value, often months after the relationship begins. The fact that you have received settlements successfully for three or six months does not mean the processor is legitimate — it may mean the build-up phase is not yet complete. Verify regulatory status, contract terms, and acquiring bank identity regardless of whether processing appears to be working.
Q8: What contract terms should I insist on before signing with any payment processor?
Every payment processing contract should contain: identification of the acquiring bank by legal entity name and registration number; explicit, itemised fee disclosure with no “fees as determined by processor” catch-all clauses; a defined settlement timeline (typically one to five business days for high-risk) with a specific breach remedy if not met; rolling reserve terms including the percentage, holding period, and release schedule with explicit contractual commitment; a dispute resolution clause specifying UK or US jurisdiction and a named arbitral institution; maximum early termination fee specified in advance; and a data protection clause specifying how your business information is processed and stored. Any contract that does not include all of these elements is either incomplete by accident (request the missing terms) or incomplete by design (treat this as a significant red flag).
Q9: How do fraudulent payment processors avoid detection for so long?
Fraudulent payment processors employ multiple concealment tactics that collectively extend their operational lifespan. They register companies in multiple jurisdictions, creating a corporate complexity that obscures beneficial ownership. They use AI-generated content to create credible-appearing websites, testimonials, and case studies. They rank prominently through paid search advertising, which does not verify the legitimacy of the advertiser’s underlying business. They specifically target high-risk merchant categories where mainstream industry press coverage is limited and merchants are less likely to share negative experiences publicly out of concern about their own industry category’s reputation. They rotate operating brands — closing and reopening under new names when complaints accumulate — while maintaining the same underlying corporate structure. The Recorded Future 2024 Annual Payment Fraud Intelligence Report noted that nearly 1,200 scam domains were linked to fraudulent merchant accounts in a single year, reflecting the scale and systematic nature of brand rotation.
Q10: What is the MATCH list and how does a fraudulent processor’s actions put my business on it?
The MATCH list (Mastercard Alert to Control High-risk Merchants) is a shared database maintained by Mastercard that acquiring banks consult during merchant onboarding to identify merchants who have been terminated for compliance or fraud-related reasons. A business can be MATCH-listed not only for its own compliance failures but also as a result of fraudulent processing activity that occurred on its behalf — including through a fraudulent MoR operator who processed transactions under the merchant’s business identity without the merchant’s knowledge. If a fraudulent aggregator processes stolen card transactions or generates excessive chargebacks under your business profile before disappearing, your business entity may find itself MATCH-listed — effectively barred from obtaining a legitimate merchant account with any Mastercard-acquiring bank for five years. MATCH listing as a result of fraudulent operator activity requires legal challenge and documentation of the fraud to secure removal. This secondary damage — being blacklisted from legitimate payment processing as a consequence of being victimised by a fraudulent processor — represents one of the most severe long-term consequences of payment processor fraud for merchants.
Comments
No comments yet. Be the first to share your thoughts.
Leave a comment